

Steve Alder


Concerns Raised About the Sharing of Health Data with Non-HIPAA Covered Entities via Apps and Consumer Devices
Earlier this month, the eHealth Initiative Foundation and Manatt Health issued a brief that calls for the introduction of a values framework to better protect health information collected, stored, and used by organizations that are not required by law to comply with Health Insurance Portability and Accountability Act (HIPAA) Rules. Health information is increasingly being collected by a wide range of apps and consumer devices. In many cases, the types of data collected by these apps and devices are the same as those collected and used by healthcare organizations. While healthcare organizations are required to implement safeguards to ensure the confidentiality, integrity, and availability of health information and uses and disclosures of that information are restricted, the same rules do not cover the data if the information is collected by other entities. It doesn’t matter what type of organization stores or uses the data. If that information is exposed it can cause considerable harm, yet this is currently something of a gray area that current regulations do not cover properly. At...
Texas Department of Aging and Disability Services Agrees to $1.6 Million Settlement Over 2015 Data Breach
The Department of Health and Human Services’ Office for Civil Rights has agreed to settle a HIPAA violation case with the Texas Department of Aging and Disability Services (DADS) to resolve HIPAA violations discovered during the investigation of a 2015 data breach that exposed the protected health information of 6,617 Medicaid recipients. The breach was caused by an error in a web application which made ePHI accessible over the internet for around 8 years. DADS submitted a breach report to OCR on June 11, 2015. OCR launched an investigation into the breach to determine whether there had been any violation of HIPAA Rules. On July 2015, OCR notified DADS that the investigation had revealed there had been multiple violations of HIPAA Rules. DADS was deemed to have violated the risk analysis provision of the HIPAA Security Rule – 45 C.F.R. § 164.308(a)(1)(ii)(A) – by failing to conduct a comprehensive, organization-wide risk analysis to identify potential risks to the confidentiality, integrity, and availability of ePHI. There had also been a failure to implement appropriate...
Class Action Lawsuit Filed Over UConn Health Phishing Attack
A class action lawsuit has been proposed which seeks to recover damages for patients whose protected health information (PHI) was exposed in the UConn Health phishing attack that was discovered on December 24, 2018. The lawsuit has been filed against the University of Connecticut and UConn Health and seeks damages, equitable, declaratory, and injunctive relief to prevent a recurrence of a data breach. A jury trial is being sought. The email accounts of multiple employees were compromised as a result of the attack. In total, 326,000 UConn Health patients had some of their personal and health information exposed in the breach. Most of the individuals affected by the breach only had a limited amount of PHI exposed, although approximately 1,500 patients had their name, address, date of birth, and Social Security number, and some medical information compromised. The lawsuit alleges UConn Health was negligent for failing to protect the private information of its patients there was a failure to provide timely, accurate, and adequate notification of the breach. The lawsuit explains there...
Superior Dental Care Patients Informed of PHI Exposure Due to Email Account Breach
The Centerville, Ohio dental insurance carrier, Superior Dental Care, has discovered an unauthorized individual has gained access to an employee’s email account and potentially viewed the protected health information of certain members. The email account breach was detected on January 23, 2019 following the identification of suspicious activity within the employee’s email account. The password for the account was immediately changed and further unauthorized access was prevented. A third-party computer forensics firm was called in to assist with the investigation and determine the nature and scope of the breach. On February 11, 2019, Superior Dental Care learned that the account had been accessed by an unidentified third party and unauthorized access to the email account was first gained on December 21, 2018. The email account contained information such as names, addresses, Social Security numbers, medical information, and payment information related to dental services received. All individuals affected by the breach have now been notified by mail and the breach has been reported to...
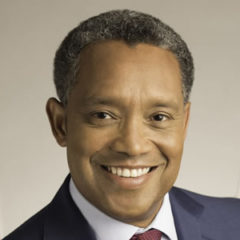
D.C. Attorney General Proposes Tougher Breach Notification Laws
Washington D.C. Attorney General Karl. A. Racine is looking to strengthen data breach notification laws to provide greater protection for D.C. residents when their personal information is exposed in a data breach. On March 21, 2019, Attorney General Racine introduced the Security Breach Protection Amendment Act, which expands the definition of personal information that warrants notifications to be sent to consumers in the event of a data breach. Currently laws in the District of Columbia require breach notifications to be sent if there has been a breach of Social Security numbers, driver’s license numbers, or financial information such as credit and debit card numbers. If passed, the Security Breach Protection Amendment Act will expand the definition of personal information to include taxpayer ID numbers, genetic information including DNA profiles, biometric information, passport numbers, military Identification data, and health insurance information. Attorney General Racine said one of the main reasons why the update was required was to better protect state residents from breaches...

Get The FREE
HIPAA Compliance Checklist
Immediate Delivery of Checklist Link To Your Email Address
Please Enter Correct Email Address
Your Privacy Respected
HIPAA Journal Privacy Policy
Get The FREE
HIPAA Compliance Checklist
Immediate Delivery of Checklist Link To Your Email Address
Please Enter Correct Email Address
Your Privacy Respected
HIPAA Journal Privacy Policy




