

Steve Alder


OCR Fines Florida Contractor Physicians’ Group $500,000 for Multiple HIPAA Compliance Failures
An HHS’ Office for Civil Rights (OCR) investigation into an impermissible disclosure of PHI by a business associate of a HIPAA-covered entity revealed serious HIPAA compliance failures. Advanced Care Hospitalists (ACH) is a Lakeland, FL-based contractor physicians’ group that provides internal medicine physicians to nursing homes and hospitals in West Florida. ACH falls under the definition of a HIPAA-covered entity and is required to comply with the HIPAA Privacy, Security, and Breach Notification Rules. ACH serves approximately 20,000 patients a year and employed between 39 and 46 staff members per year during the time frame under investigation. Between November 2011 and June 2012, ACH engaged the services of an individual who claimed to be a representative of Doctor’s First Choice billings Inc., a Florida-based provider of medical billing services. That individual used First Choice’s company name and website, but according to the owner of First Choice, those services were provided without the knowledge or permission of First Choice. A local hospital notified ACH on February 11,...
ONC Announces Winners of Easy EHR Issues Reporting Challenge
The Department of Health and Human Services’ Office of the National Coordinator for Health Information Technology (ONC) has announced the winners of its Easy EHR Issues Reporting Challenge. Currently, reporting EHR safety concerns is cumbersome and causes disruption to clinical workflows. A more efficient and user-friendly mechanism is required to allow EHR users to quickly identify, document, and report issues to their IT teams. Fast reporting of potential safety issues will allow the root causes of problems to be found more quickly and for feedback to be provided to EHR developers rapidly to ensure problems are resolved in the shortest possible timeframe. The aim of the challenge was to encourage software developers to create solutions that would help clinicians report EHR usability and safety issues more quickly and efficiently in alignment with their usual clinical workflows and make the reporting of EHR safety issues less burdensome. After assessing all submissions, ONC chose three winners: 1st Place and $45,000 was awarded to James Madison Advisory Group, which developed a...
OIG Identified Serious Security Failures at Arizona Managed Care Organizations
The Department of Health and Human Services’ Office of Inspector General (OIG) has issued a report on the findings of security audits at two managed care organizations (MCOs) in Arizona. OIG discovered serious security flaws in information systems that placed the confidentiality, integrity, and availability of Medicaid data and systems used to process Medicaid managed care claims at risk. OIG conducted the audits to determine whether the Arizona Medicaid MCOs were adequately protecting their information systems and Medicaid data, and whether they were in compliance with Health Insurance Portability and Accountability Act (HIPAA) security requirements. OIG discovered 19 security vulnerabilities in access controls and configuration management spanning 9 security control areas. 5 vulnerabilities were identified in the access controls category and 14 vulnerabilities were identified in the configuration management category. They included vulnerabilities in access controls, administrative controls, patch management, antivirus management, database management, server management, website...
7,000 Patients Affected by Georgia Spine and Orthopaedics of Atlanta Phishing Attack
Georgia Spine and Orthopaedics of Atlanta (GSOA) is notifying thousands of patients that some of their protected health information has been exposed, and potentially stolen, as a result of a phishing attack. An investigation into the data breach revealed an unauthorized individual gained access to an email account as a result of the employee responding to a phishing email. That response allowed the attacker to obtain the employee’s email account password. Third-party computer forensics experts were contracted to conduct a detailed investigation into the attack to determine the extent of the breach and find out which patients had been affected. The investigation confirmed that a single email account had been compromised on July 11, 2018. An evaluation of GSOA’s technology systems was also conducted to ensure that they were secure. In order to determine which patients had been affected, a painstaking manual analysis of all emails in the compromised account was performed to determine which messages had been accessed by the attacker. GSOA reports that the way the email account was...
DOJ Indicts Two Iranian Hackers for Role in SamSam Ransomware Attacks
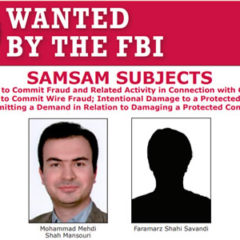
The U.S. Department of Justice has announced significant progress has been made in the investigation of the threat actors behind the SamSam ransomware attacks that have plagued the healthcare industry over the past couple of years. The DOJ, assisted the Royal Canadian Mounted Police, Calgary Police Service, and the UK’s National Crime Agency and West Yorkshire Police, have identified two Iranians who are believed to be behind the SamSam ransomware attacks. Both individuals – Faramarz Shahi Savandi and Mohammad Mehdi Shah Mansouri – have been operating out of Iran since 2016 and have been indicted on four charges: Conspiracy to commit fraud and related computer activity Conspiracy to commit wire fraud Intentional damage to a protected computer Transmitting a demand in relation to damaging a protected computer The DOJ reports that this is the first ever U.S. indictment against criminals over a for-profit ransomware, hacking, and extortion scheme. In contrast to many threat actors who use ransomware for extortion, the SamSam ransomware group conducts targeted, manual attacks on...
Your privacy respected – Read our privacy policy
Your privacy respected – Read our privacy policy




