

Steve Alder


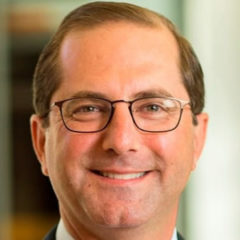
HHS Secretary Alex Azar Promises Reforms to Federal Health Privacy Rules
At a July 27 address at The Heritage Foundation, Secretary of the Department of Health and Human Services (HHS), Alex Azar, explained that the HHS will be undertaking several updates to health privacy regulations over the coming months, including updates to the Health Insurance Portability and Accountability Act (HIPAA) and 45 CFR Part 2 (Part 2) regulations. The process is expected to commence in the next couple of months. Requests for information on HIPAA and Part 2 will be issued, following which action will be taken to reform both sets of rules to remove obstacles to value-based care and support efforts to combat the opioid crisis. Rule changes are also going to be made to remove some of the barriers to data sharing which are currently hampering efforts by healthcare providers to expand the use of electronic health technology. These requests for information are part of a comprehensive review of current regulations that are hampering the ability of doctors, hospitals, and payers to improve the quality healthcare services and coordination of care while helping to reduce...
Confluence Health Informs Patients of Phishing Incident
Confluence Health, a not-for-profit health system that operates Central Washington Hospital, Wenatchee Valley Hospital and a dozen satellite clinics in Central and North Central Washington, has experienced a data security incident involving an employee’s email account that may have resulted in unauthorized accessing of patients’ protected health information. The security breach was discovered on May 29, 2018. A digital forensics firm was called in to conduct an investigation, which revealed the email account had been accessed by an unauthorized individual on May 28 and May 30, 2018. The email account only contained a limited amount of protected health information and no highly sensitive data such as Social Security numbers or financial information was exposed. Patients impacted by the incident have had information such as their names and treatment information exposed. Confluence Health had multiple security solutions in place to prevent unauthorized account access and staff had received security awareness training, yet those measures were bypassed by the attacker. While PHI access...
Lane County Health and Human Services and New England Dermatology Alert Patients to PHI Exposure
The medical records of more than 17,000 patients have been exposed in two recent incidents in Oregon and Massachusetts. Lane County Health and Human Services Alerts Patients to Loss of PHI Lane County Health and Human Services in Oregon is notifying more than 700 patients that some of their protected health information has been lost and has potentially been destroyed. 49 boxes containing patient files were moved to a temporary storage facility while the Charnelton Clinic in Eugene was being renovated. During a routine search, the boxes of files were discovered to be missing from the storage facility on June 19. Multiple teams conducted further searches for the missing boxes but they could not be located. Lane County Health and Human Services suspects the boxes of files have been destroyed along with other paperwork as part of its normal document management practice for non-medical records. However, it has not been possible to confirm whether that was definitely the case. The files contained information such as patients’ full names, addresses, telephone numbers, medical histories...
Warnings Issued Following Increase in ERP System Attacks
The United States Computer Emergency Readiness Team (US-CERT) has warned businesses about the increasing risk of cyberattacks on enterprise resource planning (ERP) systems such as the cloud-based ERPs developed by SAP and Oracle. These web-based applications are used to manage a variety of business operations, including finances, payroll, billing, logistics, and human resources functions. Consequently, these systems contain a treasure trove of sensitive data – The exact types of data sought by cybercriminals for fraud and cyber espionage. Further, many businesses rely on their ERP systems to function. A cyberattack that takes those systems out of action can have catastrophic consequences, making the systems an attractive target for sabotage by hacktivists and nation state backed hacking groups. The US-CERT warning follows a joint report on the increasing risk of ERP system attacks by cybersecurity firms Digital Shadows and Onapsis. The report focused on two of most widely used ERP systems: SAP HANA and Oracle E-Business. The authors explained that the number of publicly available...
Flowers Hospital Proposes $150,000 Settlement for 2014 Data Breach
A class action lawsuit filed in the wake of an employee-related data breach at Flowers Hospital in Dothan, Alabama in 2014 is heading towards being settled. The settlement has yet to receive final court approval, although approval seems likely and a resolution to this four-year legal battle is now in sight. In contrast to most class action lawsuits filed over the exposure/theft of PHI, this case involved the theft of data by an insider rather than a hacker. Further, the former employee used PHI for identity theft and fraud and was convicted of those crimes. The breach in question involved a former lab technician, Kamarian D. Millender, who was found in possession of paper records containing patients protected health information. Millender admitted to using the information for identity theft and for filing false tax returns in victims’ names. In December 2014, Millender was sentenced to serve two years in jail. In the class action lawsuit, filed the same year, it was claimed that between June 2013 and December 2014, paper records were left unprotected and unguarded at the hospital...

Get The FREE
HIPAA Compliance Checklist
Immediate Delivery of Checklist Link To Your Email Address
Please Enter Correct Email Address
Your Privacy Respected
HIPAA Journal Privacy Policy
Get The FREE
HIPAA Compliance Checklist
Immediate Delivery of Checklist Link To Your Email Address
Please Enter Correct Email Address
Your Privacy Respected
HIPAA Journal Privacy Policy




