Steve Alder


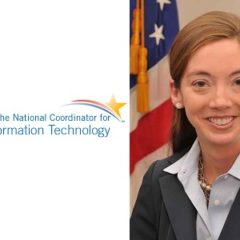
Kathryn Marchesini Appointed Chief Privacy Officer at ONC
The Office of the National Coordinator for Health IT (ONC) has a new chief privacy officer – Kathryn Marchesini, JD. The appointment was announced this week by National Coordinator Donald Rucker, M.D. Marchesini will replace Acting Chief Privacy Officer Deven McGraw, who left the position this fall. The HITECH Act requires a Chief Privacy Officer to be appointed by the ONC. The CPO is required to advise the National Coordinator on privacy, security, and data stewardship of electronic health information and to coordinate with other federal agencies. Following the departure of McGraw, it was unclear whether the position of CPO would be filled at the ONC. The ONC has had major cuts to its budget, and in an effort to become a much leaner organization, funding for the Office of the Chief Privacy Officer was due to be withdrawn in 2018. However, the decision has been taken to appoint a successor to McGraw. There are few individuals better qualified to take on the role of CPO. Katheryn Marchesini has extensive experience in the field of data privacy and security, having spent seven...
Data Breach Notification Bill Introduced in North Carolina
A new data breach notification bill has been introduced in North Carolina in response to the rise in breaches of personal information in 2017. Last year, more than 5.3 million residents of North Carolina were impacted by data breaches. The rise in data breaches prompted state Attorney General Josh Stein and state Representative Jason Saine to introduce the Act to Strengthen Identity Theft Protections. If passed, North Carolina will have some of the toughest data breach notification laws in the United States. The Act, introduced on January 8, 2018, is intended to strengthen protections for state residents. The Act updates the definitions of personal information and security breaches and decreases the allowable time to notify state residents of a breach of their personal information. The definition of personal information has been expanded to include insurance account numbers and medical information. It is currently unclear whether the new law will apply to organizations covered by the Health Insurance Portability and Accountability Act (HIPAA) or if they will be deemed to be in...
43,000 Patients of Coplin Health Systems Potentially Impacted by Laptop Theft
West Virginia-based Coplin Health Systems has informed 43,000 patients that their PHI has potentially been exposed as a result of the theft of an unencrypted laptop computer from the vehicle of an employee. Coplin Health was alerted to the theft on November 2, 2017. The theft was immediately reported to law enforcement and an investigation was launched, although at the time of issuing notifications, the laptop computer has not been recovered. While it is possible that protected health information of patients was stored on the laptop, Coplin Health does not believe that was the case, although the possibility of data exposure cannot be ruled out with 100% certainty. Coplin Health notes that the laptop had various security protections in place to ensure the privacy of patients in the event of the laptop being stolen. While the laptop could potentially be used to gain access to patient data, a password would have been required and it is not suspected that the thief had “the sophisticated knowledge and resources necessary to bypass the laptop’s security mechanisms.” Further, Coplin...
St. Rose Dominican Hospital Patients Impacted by DJO Global PHI Breach
DJO Global, a provider of medical technologies to help patients maintain and regain natural motion, has discovered that some patients’ information has been exposed, and potentially disclosed, to unauthorized individuals. Individuals who had received a DJO Global device in the emergency room, Urgent Care Site, or the Same Day Surgery Center of the Siena, San Martin or De Lima campuses of St. Rose Dominican Hospital in Las Vegas, NV between July 17 and October 16, 2017 have potentially been affected. Those individuals are likely to have signed a DJO Global Patient Product Agreement confirming they had received one of the company’s devices. Those consent forms should have been sent to DJO Global; hhowever, a batch of consent forms was not received. A DJO employee collected the forms from St. Rose Dominican Hospital and should have taken them to DHL to be delivered to DJO Global; however, the forms were lost in transit. They are believed to have been lost between collection from the hospital and delivery to DHL. The forms contained the following information: Name, phone number,...
Lack of Encryption on Hard Drive Results in the Exposure of 9387 Patients’ PHI
Framingham, MA-based Charles River Medical Associates has discovered the danger of failing to use encryption to protect data stored on portable hard drives. In late November, the practice discovered one of its portable hard drives was missing. The device contained x-ray images, names, patient ID numbers, and birth dates. Every patient who had visited the Framingham radiology lab for a bone density scan since 2010 had their x-ray images exposed – almost 9,400 individuals. The hard drive was used by the practice as a backup device and updated the stored data each month with bone density scans from the past four weeks. The last time the device was used was for the October data backup. In late November, when the monthly backup was scheduled to be made, the portable drive could not be found. A full search of the premises was conducted, which took several weeks, but the device could not be located. All staff members were questioned about the whereabouts of the drive, but no one had seen the device in the past four weeks. Charles River Medical Associates has now declared the device lost...
Your privacy respected – Read our privacy policy
Your privacy respected – Read our privacy policy