

Steve Alder


Estill County Chiropractic Patients Impacted by Ransomware Attack
On January 17, 2017, Irvine, KY-based Estill County Chiropractic discovered its computer system had been breached by an unauthorized individual who encrypted files with ransomware . An external computer consultant was hired to conduct a thorough investigation of the incident to determine how the ransomware was installed and the extent of the attack. While many ransomware infections occur as a result of an employee responding to a malicious spam email message, in this case, the attacker was discovered to have previously gained access to Estill County Chiropractic’s computer system. Access to the system was first gained on January 6, 2017, although the ransomware was not installed until January 17. Due to the nature of the attack, it is possible the attacker gained access to the protected health information of patients and stole patient data. The information potentially accessed included patients’ names, addresses, phone numbers, email addresses, dates of birth, clinical information, Social Security numbers, medical diagnoses, provider notes, claims information and health plan...
SAFER Guides Updated by ONC: Ransomware Prevention and Mitigation Strategies Included
The Department of Health and Human Services’ Office of the National Coordinator for Health Information Technology (ONC) has updated its SAFER Guides to include information to help healthcare providers protect against ransomware infections and mitigate ransomware attacks. The Safety Assurance Factors for Electronic Health Record Resilience (SAFER) Guides were first released in January 2014 to help healthcare providers improve the usability of their EHRs and address the risks that EHR technology can introduce. The SAFER Guides can also be used to reduce the potential for patients to suffer EHR-related harm. The SAFER Guides cover a range of key focus areas and include evidence-based best practices that can be adopted by healthcare providers to improve the usability and safety of their EHRs. Over the past three years, technology has changed as have the threats faced by the healthcare industry. The guides were therefore due an update to keep them useful and relevant. Prior to issuing the updated guides, ONC sought feedback from healthcare providers and developers of EHRs. The comments...
Former Employee Accused of Stealing PHI of up to 160,000 Med Center Health Patients
The Kentucky-based 6-hospital health system Med Center Health has reported a data breach affecting approximately 160,000 patients. Med Center Health believes a former employee may have stolen patients’ protected health information (PHI) prior to leaving employment. The former employee has been accused of stealing PHI including names, addresses, health insurance information, Social Security numbers, procedure codes and billing information. Medical records were not compromised at any point. The FBI has been notified and is also investigating along with other federal agencies. Med Center health is in the process of notifying patients of the breach, although the process is expected to take a couple of weeks due to the number of individuals that have been impacted. While the breach has only recently been announced, the data theft incidents date back to 2014 and 2015. The former employee is understood to have taken an encrypted CD and encrypted portable storage device in August 2014 and February 2015. There was no legitimate work reason for ePHI to have been taken, although on both...
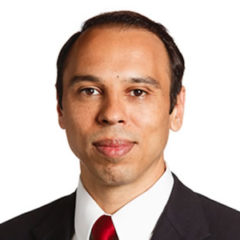
Roger Severino Named New Director of HHS’ Office for Civil Rights
The Department of Health and Human Services’ Office for Civil Rights has a new leader. The Trump Administration has chosen former civil rights trial attorney Roger Severino to lead the HIPAA enforcement efforts of the Office for Civil Rights. Severino joins OCR from the Heritage Foundation’s DeVos Center for Religion and Civil Society, Institute for Family, Community, and Opportunity, where he served as Director since May 2015. A formal announcement about the appointment of the new OCR Director has yet to be issued; however, the Heritage Foundation has confirmed that Severino is no longer on the staff and his name has been added to the HHS website. A spokesperson for OCR has also confirmed that Severino will be the new director and Severino’s LinkedIn profile has also been updated to include his new position as OCR chief. Severino has a background in civil rights litigation, having worked as a trial attorney for the Department of Justice for seven years in the Housing and Civil Enforcement division. During his time at the DOJ, Severino enforced the Fair Housing Act, Title II...
Urology Austin Ransomware Attack Announced
Urology Austin has started notifying 279,663 patients that some of their protected health information may have been impacted in a recent ransomware attack. Potentially, the attackers gained access to names, addresses, dates of birth, medical information and the Social Security numbers of patients. The attack occurred on January 22, 2017, although rapid detection of the incident limited the damage caused. Within minutes of the attack, the computer network was shut down to prevent the spread of the infection and potential access/exfiltration of PHI. However, even with the fast response, data stored on the organization’s servers were encrypted. Ransomware often blindly encrypts data. The attacks are intended to cause major disruption to patient services to force an organization into paying a ransom demand to obtain a key to unlock the encryption. Data are not accessed or stolen by the attackers. The risk of patients’ protected health information being accessed and misused after this type of attack is often low. In this case, the decision was taken to provide identity theft monitoring...

Get The FREE
HIPAA Compliance Checklist
Immediate Delivery of Checklist Link To Your Email Address
Please Enter Correct Email Address
Your Privacy Respected
HIPAA Journal Privacy Policy
Get The FREE
HIPAA Compliance Checklist
Immediate Delivery of Checklist Link To Your Email Address
Please Enter Correct Email Address
Your Privacy Respected
HIPAA Journal Privacy Policy




