

Steve Alder


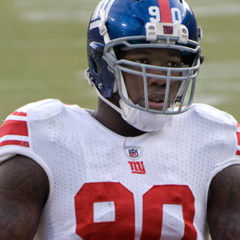
Jason Pierre-Paul Finger Amputation Disclosure Violates HIPAA Rules
to a news report on ESPN. Surgeons treated the football player after the accident, but were unable to save his right index finger. A tragedy such as this would naturally make then news; however, it is making headlines for another reason. Information about Pierre-Paul’s medical condition appears to have been leaked to the media from a source within the hospital; breaching the Health Insurance Portability and Accountability Act (HIPAA) and violating Pierre-Paul’s right to privacy. The circumstances surrounding the disclosure strongly suggest there was no prior consent obtained from Pierre-Paul before the information was disclosed; even the New York Giants were unaware their defensive end had a digit removed until they heard the report on ESPN. ESPN Reports on Pierre-Paul’s Medical Status The news broke on Sunday after a healthcare worker at the hospital disclosed the news about the celebrity patient to a friend; violating Pierre-Paul’s privacy and breaching HIPAA Rules. That friend then posted the information online via his Twitter account, and from there rumors started...
State Data Breach Laws Should Preempt Federal Laws, Says NAAG
Yesterday, the National Association of Attorneys General (NAAG) sent a letter addressed to congressional leaders urging them to consider the state laws that have been put in place to protect consumers, and not to diminish the role that state Attorneys General play in enforcing data security and protection laws. The letter urges congress not to make changes to federal data breach notification and data security laws that would lessen the protections that have been put in place by the states. The letter calls for congress to refrain from introducing data security and data breach notification laws that pre-empt those introduced in each state. There are a number of bills pending which include data security and breach notification requirements that would pre-empt state laws. A Similar Request Was made A Decade Ago This is not the first time the NAAG has written to congress on state security breach notification laws; a similar request was made in 2005. In that letter it was argued that “Pre-emption interferes with state legislatures’ democratic role as laboratories of...
New Mobile Malware Appearing at Rate of 4,900 per Day
The threat from malware, phishing and spear phishing campaigns has been widely reported in recent months. Numerous new strains of dangerous malware have been identified this year and the past few weeks have seen the FBI issue warnings on two malware strains; Sakula and Stegoloader; two particularly worrying pieces of malware that are currently being used by cybercriminals to gain access to healthcare data and financial information. The scale of the threat is difficult to estimate; however a new study on mobile malware offers an indication of just how serious the problem is. The report from Security firm, G Data, indicates new malware strains are appearing at a rate of nearly 5,000 per day. According to the report, the firm collected over 200 new android malware samples on average every hour in the first quarter of the year. 440,000 new strains of Android malware were discovered in Q1, 2015, representing a 6.4% increase compared to Q4 of 2014: A jump of 21% from corresponding period last year. In Q1 more than double the volume of malware was discovered than in the whole of 2011 and...
Stolen UCSF Laptops Contained PHI of Research Participants
The University of California San Francisco (UCSF) has announced the burglary of a faculty member’s office involved the theft of a laptop computer containing unencrypted, protected health data. The information stored on the device included research and health information along with Personally Identifiable Information (PII) and medical insurance details. The burglary occurred in May, with thieves gaining access to the office of a faculty member of the Cardiac Electrophysiology & Arrhythmia Service. UCSF discovered the theft, and potential data breach, on May 6, 2015. After conducting an investigation UCSF determined that the data stored on the laptop included names, dates of birth, medical record numbers, and health insurance Identification numbers. No Social Security numbers or financial information were exposed, although UCSF’s investigation revealed that 435 individuals had their health information compromised. In the notice placed on the University website, the incident is stated to have involved the theft of a laptop computer. However, the notice says “UCSF promptly began an...
Rhode Island Identity Theft Protection Act Updates Breach Notification Laws
State Governor, Gina Raimondo, has added her signature to Senate Bill S0134; otherwise known as the Rhode Island Identity Theft Protection Act (2015). Rhode Island follows other states that have already introduced enhanced data protection and breach notification laws this year; neighboring Connecticut being one of the most recent. The new act has been introduced to improve protections for state residents and a considerable number of changes have been made to existing state laws. The new Act will become enforceable on June 26, 2016. The new law requires any “person” –individual or organization – that does business in the state of Rhode Island, and “stores, collects, processes, maintains, acquires, uses, owns or licenses personal information about a Rhode Island resident” must ensure that it puts “a risk-based information security program” in place to protect the data held. The Act requires this “in order to protect the personal information from unauthorized access, use, modification, destruction or disclosure.” The exact protections that must be put in place are not stipulated,...

Get The FREE
HIPAA Compliance Checklist
Immediate Delivery of Checklist Link To Your Email Address
Please Enter Correct Email Address
Your Privacy Respected
HIPAA Journal Privacy Policy
Get The FREE
HIPAA Compliance Checklist
Immediate Delivery of Checklist Link To Your Email Address
Please Enter Correct Email Address
Your Privacy Respected
HIPAA Journal Privacy Policy




