

Steve Alder


Liberty Resources Announces July 2024 Data Breach
Liberty Resources, a Syracuse, NY-based human services agency, has announced a security incident that was first identified 16 months ago, on July 22, 2024. Liberty Resources said an immediate and thorough investigation was conducted, and that the investigation into the incident is still ongoing. It is unclear why the investigation has taken so long. According to its website data breach notice, the specific information compromised in the incident has yet to be confirmed. Employees and patients have been warned that the impacted data likely includes names, addresses, dates of birth, Social Security numbers, medical information, and health insurance information. Since the investigation has not yet concluded, it is unclear how many individuals have been affected. While no evidence has been found to indicate any misuse of the affected information, employees and clients have been advised to remain vigilant against identity theft and fraud. While not stated by Liberty Resources, this appears to have been a cyberattack by the Rhysida threat group, which added Liberty Resources to its data...
Kaiser Permanente Agrees to Pay Up to $47.5 Million to Settle Web Tracker Litigation
The Oakland, CA-based healthcare giant Kaiser Permanente has agreed to pay up to $47.5 million to settle class action litigation over its use of tracking technologies on its websites, patient portals, and mobile applications. This is one of the largest settlements to be agreed to resolve claims stemming from the use of tracking tools by a healthcare organization. Kaiser disclosed the data breach last year following a voluntary internal investigation into its use of tracking technologies, which confirmed that up to 13.4 million individuals had potentially been affected – the second-largest healthcare data breach to be announced in 2024. Kaiser removed the tracking tools from its websites and mobile applications out of an abundance of caution and sent notifications to all potentially affected individuals. Kaiser also engaged experts and, based on their guidance, implemented additional safeguards to prevent similar privacy breaches in the future. Website tracking technologies, such as pixels, are used extensively on websites to track user activity. They can provide website owners with...
High Severity Vulnerabilities Patched in Mirion Medical EC2 Software NMIS BioDose
Mirion Medical has issued patches to fix five high-severity vulnerabilities in its EC2 Software NMIS BioDose software. Successful exploitation of the vulnerabilities could allow an attacker to gain unauthorized access to the application, modify program executables, access sensitive information, and potentially remotely execute code. Mirion Medical EC2 Software NMIS BioDose is tracking software used by healthcare providers to keep track of inventory, doses, patient information, and billing. The vulnerabilities affect software versions prior to v23.0. Users have been urged to update to v23.0 or later versions to prevent the vulnerabilities from being exploited. Users with an active support contract can update to the latest version via the software. At the time of issuing the updated version, there had been no known exploitation of the vulnerabilities in the wild. CVE-2025-64298 – CVSS v3.1: 8.4 | CVSS v4: 8.6 NMIS/BioDose V22.02 and previous version installations where the embedded Microsoft SQL Server Express is used are exposed in the Windows share accessed by clients in networked...
What is the HITECH Act?
The Health Information Technology for Economic and Clinical Health Act or HITECH Act is the part of the American Recovery and Reinvestment Act of 2009 that incentivized the meaningful use of EHRs and strengthened the privacy and security provisions of HIPAA. Among other measures, the HITECH Act extended the reach of HIPAA to business associates of covered entities, who were now accountable for failures of HIPAA compliance. The Act also introduced tougher penalties for violations of HIPAA. This article explains HITECH in depth. Get a copy of our HITECH Act & HIPAA Checklist to see the 20 ways The HITECH Act affected HIPAA and what is required for HIPAA Compliance. Summary Of Article Contents What are the Goals of the HITECH Act? The HITECH Act And ARRA HITECH Act Importance HITECH Act Summary HITECH Act Compliance Date The Meaningful Use Program Business Associates Tougher Penalties What are the Goals of the HITECH Act? The five HITECH Act goals have been described as the five goals of the US healthcare system: Improve quality, safety, and efficiency Engage patients in their...
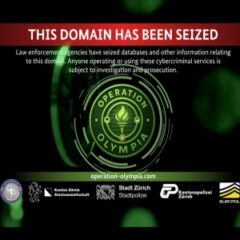
Europol Takes Down Illegal Crypto Mixing Laundering Service Used by Ransomware Actors
A cryptocurrency mixing service used by criminals to launder the proceeds from their illegal activities has been shut down by Europol, Eurojust, and law enforcement agencies in Switzerland and Germany. Cybercriminals, such as ransomware actors, typically receive payment for their attacks in cryptocurrency. Cryptocurrency transactions are not anonymous, as all transactions are recorded on the public blockchain and can be traced to the wallets receiving the funds. That means the proceeds from cybercrime can be traced to individuals if the wallet address is linked to a real-world identity. Cybercriminals use cryptocurrency mixing services to launder the proceeds from their attacks, then redirect their anonymized funds to cryptocurrency exchanges to cash out. The law enforcement operation was a week-long effort – Operation Olympia – between November 24 and November 26, targeting Cryptomixer, an illegal cryptocurrency mixing service that law enforcement agencies have been trying to shut down since its creation in 2016. According to Europol, Cryptomixer was the mixing service of...

Get The FREE
HIPAA Compliance Checklist
Immediate Delivery of Checklist Link To Your Email Address
Please Enter Correct Email Address
Your Privacy Respected
HIPAA Journal Privacy Policy
Get The FREE
HIPAA Compliance Checklist
Immediate Delivery of Checklist Link To Your Email Address
Please Enter Correct Email Address
Your Privacy Respected
HIPAA Journal Privacy Policy




