

Steve Alder


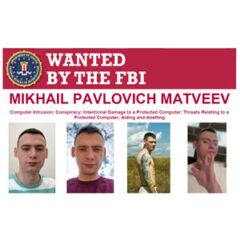
Russia Arrests Alleged HIVE/LockBit Ransomware Actor Wanted by FBI
Ransomware actors operating within Russia are beyond the reach of Western law enforcement agencies and appear to operate without fear of arrest, providing they do not conduct any attacks within Russia or the Commonwealth of Independent States (CIS); however, a suspected member of multiple ransomware groups has been arrested in Russia, according to Russian media. RIA Novosti has reported that a “programmer” wanted by the Federal Bureau of Investigation (FBI) in connection with U.S. ransomware attacks has been arrested by Russian authorities. Suspected Russian cybercriminal, Mikhail Pavlovich Matveev, was indicted by the U.S. Department of Justice (DoJ) in May 2023 and is alleged to have been a central figure in three ransomware groups. Matveev was charged in the United States in connection with ransomware attacks on the U.S. government, hospitals, & schools, including a law enforcement agency and a behavioral healthcare provider in New Jersey, and a police department in Washington D.C. As a member of the LockBit, Hive, and Babuk ransomware operations, Metveev is alleged to...
PHIPA Compliance Checklist
A PHIPA compliance checklist is a document that can help health information custodians comply with Ontario’s Personal Health Information Protection Act (PHIPA) – an Act that standardizes how personal health information is protected across the health sector and designed to give individuals greater control over how their personal health information is collected, used, and disclosed. Compliance with PHIPA is mandatory for persons and organizations defined as health information custodians (“custodians”) in the Act. Custodians include – but are not limited to – hospitals, care homes, psychiatric care facilities, pharmacies, and healthcare practitioners not employed by a hospital or other healthcare facility – for example, school nurses and sports team doctors. Custodians not only have to comply with PHIPA, but ensure that their agents (employees, students, volunteers, etc.) comply with PHIPA – along with other organizations who provide a service on the custodian´s behalf when the service collects, uses, modifies, discloses, retains, or disposes of personal health information. This...
Patient Data Compromised in Cyberattack on New York Women’s Healthcare Providers
Protected health information has been exposed in cyberattacks at Visiting Physician Services of Michigan, Physicians’ Primary Care of Southwest Florida, and Maternal Fetal Medicine Associates, Carnegie Hill Imaging for Women, Carnegie Women’s Health, and Equinox Inc. in New York. Maternal Fetal Medicine Associates | Carnegie Hill Imaging for Women | Carnegie Women’s Health – New York Patients of Maternal Fetal Medicine Associates, Carnegie Hill Imaging for Women, and Carnegie Women’s Health in New York have been affected by a security incident that involved unauthorized access and the potential theft of their personal and health information. The practices identified unauthorized access to their computer network on September 16, 2024, which the forensic investigation confirmed began on July 30, 2024, and lasted until September 16, 2024. During that time there was unauthorized access to files and certain files were downloaded without authorization; however, the threat actor did not access the electronic medical record database. The file review is ongoing, so it has yet to be...
At Least 43% of Covered Entities Still Not Using Software for HIPAA Compliance Tracking
A recent survey conducted by The HIPAA Journal found that 57% of HIPAA-covered entities now use HIPAA compliance software to manage their HIPAA compliance programs. While this figure highlights progress toward streamlined compliance management, it also reveals a concerning reality: at least 43% of organizations still rely on manual processes or potentially do not track compliance at all. The survey respondents were subscribers to The HIPAA Journal newsletter, a group likely more invested in HIPAA compliance than the average healthcare organization. This selection bias suggests the actual percentage of organizations not using compliance software may be significantly higher. Despite HIPAA regulations mandating that covered entities maintain detailed compliance records for several years, many organizations continue using paper-based systems or fragmented manual processes. These outdated methods can lead to inconsistent record-keeping, increased administrative burdens, and heightened risks of non-compliance. HIPAA compliance software simplifies managing security policies, training...
Survey Finds Over 90% of Organizations Now Provide Annual HIPAA Refresher Training
A recent survey conducted by The HIPAA Journal reveals that over 90% of organizations now provide annual HIPAA refresher training to all staff exposed to protected health information (PHI). This encouraging statistic underscores a growing commitment to HIPAA compliance, though the survey’s context suggests some caution in interpreting the results. The survey targeted subscribers of The HIPAA Journal newsletter, a group inherently invested in HIPAA compliance. These individuals likely represent organizations with well-established privacy and security protocols. This respondent profile could skew the results toward higher reported compliance rates compared to the broader healthcare industry. Despite this potential bias, the findings highlight the significance placed on regular HIPAA training. In an era of increasing cybersecurity threats and regulatory scrutiny, continuous education on PHI protection is critical for reducing the risk of data breaches and compliance violations. HIPAA Training for Employees Our training provides employees with a clear and practical understanding of...

Get The FREE
HIPAA Compliance Checklist
Immediate Delivery of Checklist Link To Your Email Address
Please Enter Correct Email Address
Your Privacy Respected
HIPAA Journal Privacy Policy
Get The FREE
HIPAA Compliance Checklist
Immediate Delivery of Checklist Link To Your Email Address
Please Enter Correct Email Address
Your Privacy Respected
HIPAA Journal Privacy Policy




