

Steve Alder


Only 49% of Critical Infrastructure Entities Acted on CISA Ransomware Vulnerability Warnings
In late 2022, the U.S. Cybersecurity and Infrastructure Security Agency (CISA) launched a Ransomware Vulnerability Warning Pilot (RVWP) program that involved sending warnings to critical infrastructure entities when vulnerabilities were identified in their internet-facing devices. The program concentrated on vulnerabilities that were known to have been exploited by ransomware groups. CISA conducts scans of internet-exposed devices to identify known vulnerabilities that could potentially be exploited. If a vulnerability is detected on an internet-accessible device, CISA proactively sends a warning to allow action to be taken to correct the vulnerability before it can be exploited. When the pilot commenced, many warnings were sent about the ProxyNotShell vulnerabilities, which were being actively exploited by ransomware groups. According to Verizon’s 2024 Data Breach Investigations report, there has been a 180% YoY increase in cyberattacks that used vulnerability exploitation for initial access. Ransomware groups are actively seeking vulnerabilities to exploit and are finding plenty...
Settlement Proposed to Resolve Gifted Healthcare Data Breach Lawsuit
Gifted Healthcare has proposed a settlement to resolve a class action lawsuit that alleged negligence for failing to implement reasonable cybersecurity measures, resulting in a data breach. The Metairie, LA-based nursing agency identified suspicious activity in an employee email account and the forensic investigation confirmed that three email accounts had been accessed by unauthorized individuals between August 25, 2021, and December 10, 2021. The review of the accounts was completed in July 2022 and confirmed that the personal information of 13,221 prospective, current, and former employees had been exposed, including names, Social Security numbers, and financial account information. A class action lawsuit – Cheryl Covington V. Gifted Nurses LLC d/b/a Gifted Healthcare – was filed in response to the breach that alleged the plaintiff and class suffered injuries from the misuse of their data, including fraudulent attempts to open bank accounts, decreased credit scores, and out-of-pocket expenses spent on mitigation measures. The lawsuit also alleged the victims of the...
Connecticut Lawmakers Pass Bill to Improve Preparedness for Cyberattacks and Safety for Home Health Care Workers
On May 6, 2024, lawmakers in Connecticut passed a bill that improves protections for home care workers and requires healthcare facilities to demonstrate they have a plan for responding to cyberattacks. The House passed the bill with a vote of 112-37 and it now awaits Governor Ned Lamont’s signature. The home healthcare worker provisions of the bill were prompted by the attempted sexual assault and murder of visiting nurse Joyce Grayson, who was killed by a convicted sex offender in October 2023 while she was working at a halfway house in Willimantic. The bill requires home health agencies to collect information on clients, such as if they have a history of violence against healthcare workers, domestic abuse, and substance use, as well as information on their psychiatric history, if there are weapons or safety hazards in their homes and the crime rate in the area where they live. That information must be made available to any employee assigned to clients, but healthcare agencies are not permitted to deny services to clients based on the information collected. The bill also requires...
DocGo Says Patient Data Stolen in Recent Cyberattack
DocGo, a provider of mobile medical services and transportation in 26 US states and the United Kingdom, has announced that it has fallen victim to a cyberattack in which patient data was stolen. In a filing with the US Securities and Exchange Commission (SEC), DocGo explained that the attack targeted systems used to support its ambulance transportation business. The breach was rapidly contained, the threat actor has been removed from its systems, and a third-party cybersecurity company has been assisting with the investigation. The security breach was limited to DocGo’s ambulance transportation business and no other business lines were affected. DocGo said the incident has had no significant effect on its overall financial condition. The attackers obtained a limited number of healthcare records of patients who used its ambulance service, and notifications are now starting to be sent to those individuals. DocGo has not publicly stated how many patients have been affected nor the types of data compromised in the incident. At this stage, no threat actors appear to have claimed...
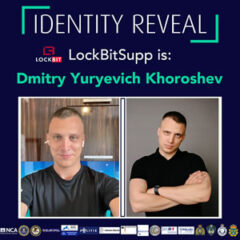
LockBit Leader Named and Sanctioned
The UK’s National Crime Agency (NCA) has named the leader of the infamous LockBit ransomware group as Russian national Dmitry Yuryevich Khoroshev, also known as LockBitSup. Lockbit is a ransomware-as-a-service group that has been in operation for four years. During that time, the group became the most prolific ransomware operation and targeted thousands of companies worldwide. According to the U.S. Department of Justice, LockBit has claimed more than 2,000 victims worldwide, has obtained more than $500 million in ransom payments, and has caused billions of dollars in losses. In February 2024, an international law enforcement operation – Operation Cronos – headed by the NCA successfully infiltrated the group’s systems, took control of its infrastructure, and locked the group out of its systems. The NCA took control of the group’s administrative systems, which the group’s affiliates used to conduct ransomware attacks, and the group’s public-facing data leak site where victims are named and stolen data are published. According to the NCA, information was gathered on LockBit’s 194...

Get The FREE
HIPAA Compliance Checklist
Immediate Delivery of Checklist Link To Your Email Address
Please Enter Correct Email Address
Your Privacy Respected
HIPAA Journal Privacy Policy
Get The FREE
HIPAA Compliance Checklist
Immediate Delivery of Checklist Link To Your Email Address
Please Enter Correct Email Address
Your Privacy Respected
HIPAA Journal Privacy Policy




