

July 2026 Healthcare Data Breach Report
In July 2026, 77 healthcare data breaches affecting 500 or more individuals were reported to the U.S. Department of Health and Human Services (HHS) Office for Civil Rights. July was the third consecutive month in which large healthcare data breaches increased, with a month-over-month increase of 10%.
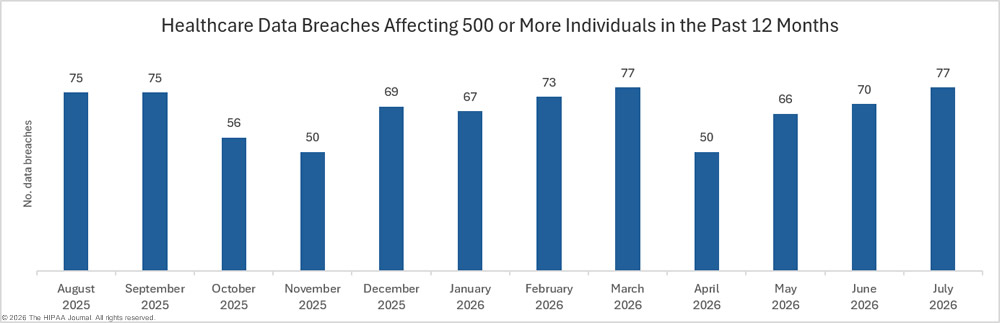
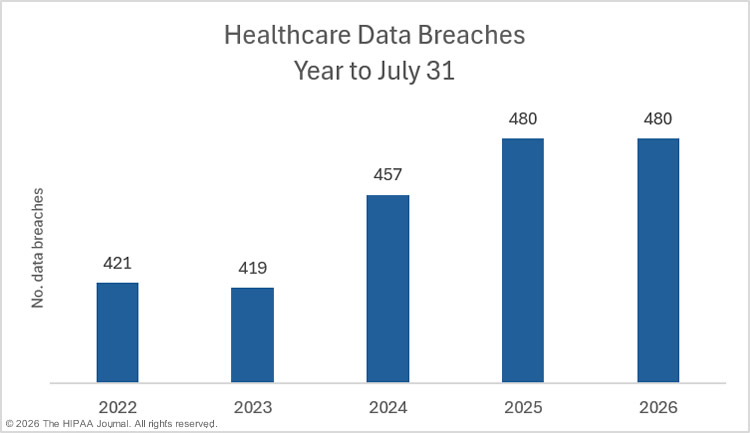
Last year was a record-breaking year for healthcare data breaches. The OCR data breach portal currently shows 806 large healthcare data breaches in 2025 – an increase of 8.6% from 2024. While 2026 was looking like there would be a fall in large healthcare data breaches, the year-to-date figures now suggest otherwise. The exact same number of data breaches are listed on the OCR data breach portal for January to July as this time in 2025, and it is likely that some breaches have yet to be added to the portal.
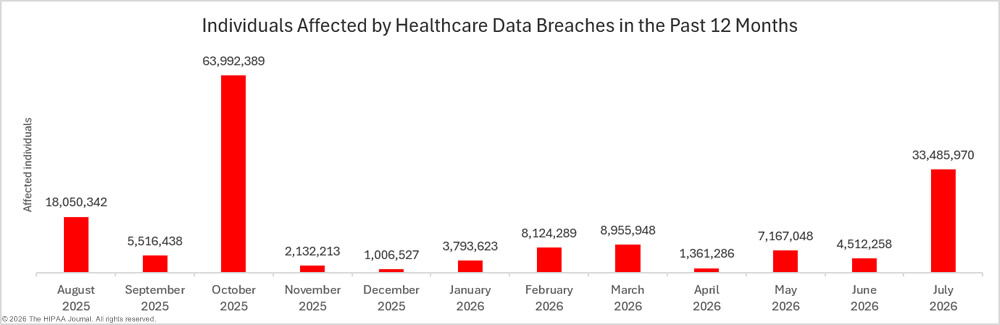
July was the worst month since October 2025 in terms of individuals affected by healthcare data breaches. Across the 77 large data breaches, the protected health information of at least 33,485,970 individuals was exposed or impermissibly disclosed – an increase of 642% from June 2026, and 154% higher than the 12-month average of 13.2 million individuals per month.
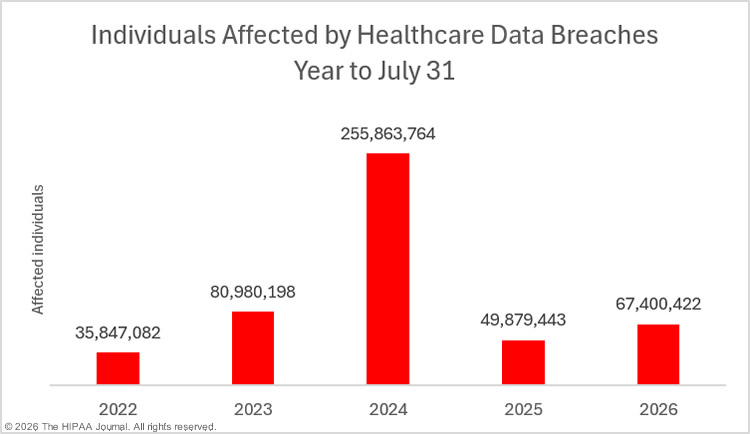
The year-to-date figures show an increase in breach severity year-over-year. Between January and July 2026, the protected health information of 67,400,422 individuals was exposed or impermissibly disclosed; an increase of 35.1% from this time last year.
Biggest Healthcare Data Breaches in July 2026
In July, 23 security incidents were reported to OCR involving the protected health information of 10,000 or more individuals, including four very large data breaches that each affected more than 1 million individuals. One of the incidents was the 4th largest healthcare data breach of all time to be reported by a single HIPAA-regulated entity, affecting an estimated 15 million individuals. The four biggest healthcare data breaches in July affected more than 32 million individuals – more than 9% of the population of the United States.
The largest data breach occurred at DentaQuest, a Sun Life U.S-owned dental and vision benefits administrator, which fell victim to a cyberattack by the notorious data theft and extortion group ShinyHunters. In early June 2026, DentaQuest announced that it was investigating a cybersecurity incident involving a limited part of its computer network. The threat group had access to its network for around 3 days in May 2026. ShinyHunters claimed responsibility and said 234 GB of data was exfiltrated in the incident, then started leaking the stolen data as it failed to reach an agreement with DentaQuest on a ransom payment. The leak included around 2.6 million unique email addresses, and the breach was reported to OCR as affecting an estimated 15 million individuals. That total may increase as the investigation progresses.
The next three largest data breaches all occurred at business associates of HIPAA-covered entities. Aesto Health, a healthcare technology company that offers secure data migration, legacy data archiving, and electronic health record (EHR) exchanges, experienced a hacking incident that affected at least 39 of its healthcare clients and involved the protected health information of more than 9.5 million individuals. The incident occurred in December 2025 and involved unauthorized access to its AWS environment. No threat group appears to have claimed responsibility.
Unlimited Technology Systems, an Ohio-based revenue cycle management and practice management software company, discovered its network had been accessed by an unauthorized third party for five days in October 2025, and potentially obtained the protected health information of more than 3.8 million individuals. A similar-sized data breach was reported by CareCloud, a provider of cloud-based and AI-powered EHR, RCM, PM, and clinical documentation solutions, which discovered that a threat actor accessed its AWS environment over 6 days in March 2026, and likely exfiltrated databases containing the protected health information of more than 3.7 million individuals. As with the incident at Unlimited Technology Systems, no threat group appears to have claimed responsibility.
| Regulated Entity | State | Covered Entity Type | Individuals Affected | Cause of Breach |
| DentaQuest, LLC | MA | Health Plan | 15,000,000 | Hacking incident (ShinyHunters data theft and extortion group) |
| Aesto, LLC | AL | Business Associate | 9,540,683 | Hacking incident |
| Unlimited Technology Systems, LLC | OH | Business Associate | 3,803,750 | Hacking incident |
| CareCloud, Inc. | NJ | Business Associate | 3,756,469 | Hacking incident |
| Lifespan Physician Group of Massachusetts, Inc. d/b/a Brown Health Medical Group-MA | MA | Healthcare Provider | 311,760 | Hacking incident |
| One Medical Group, Inc. | CA | Healthcare Provider | 153,174 | Hacking incident (ShinyHunters data theft and extortion group) |
| Madera Community Hospital | CA | Healthcare Provider | 150,810 | Hacking incident |
| zHealth, Inc. | CA | Business Associate | 118,563 | Ransomware attack (Kazu ransomware group) |
| Boundary Regional Community Health Center dba Kaniksu Community Health | ID | Healthcare Provider | 88,000 | Hacking incident at business associate Aesto (see above) |
| A-O-M-S, P.L.L.C. d/b/a Arkansas Oral & Maxillofacial Surgeons | AR | Healthcare Provider | 64,831 | Hacking incident (PEAR data theft and extortion group) |
| Casper Orthopedic Associates, PC | DC | Healthcare Provider | 56,197 | Hacking incident |
| Heart Care Centers of Illinois | IL | Healthcare Provider | 52,562 | Email phishing incident |
| Sunshine Health | FL | Health Plan | 41,569 | Vishing (voice phishing) incident |
| Brookhaven ENT Allergy and Facial Surgery | MS | Healthcare Provider | 30,403 | Hacking incident at vendor CloudCare |
| Alta Orthopaedics Medical Group, Inc. | PA | Healthcare Provider | 24,496 | Ransomware attack (INC Ransom ransomware group) |
| Nephrology Associates, M.D., P.A. | KS | Healthcare Provider | 24,088 | Ransomware attack (The Gentlemen ransomware group) |
| Jeffrey David Reuben, M.D. | TX | Healthcare Provider | 17,017 | Hacking incident |
| Regional Center of Orange County | CA | Business Associate | 16,545 | Improper disposal of paper records by janitorial service provider |
| ZenPatient, Inc. | CA | Healthcare Provider | 15,749 | Hacking incident (data theft confirmed) |
| Cornerstone Behavioral Healthcare | ME | Healthcare Provider | 14,830 | Ransomware attack (Group unknown) |
| Resource Center of Dallas, Inc. | TX | Healthcare Provider | 12,490 | Hacking incident |
| Agave Dental-Floresville | TX | Healthcare Provider | 11,790 | Ransomware attack (The Gentlemen ransomware group) |
| Any-Time Home Care, Inc. | NY | Healthcare Provider | 11,753 | Hacking/IT Incident |
When the number of affected individuals is not known by the HIPAA Breach Notification Rule reporting deadline, OCR should be provided with an estimate. The total can then be amended when the data review is completed. It is common for regulated entities to provide an “estimate” of 500 or 501 individuals, as appears to be the case with seven of the breaches reported in July.
| Regulated Entity | State | Covered Entity Type | Individuals Affected | Type of Breach |
| Open Door Health Center of Illinois | WA | Healthcare Provider | 501 | Network server hacking incident (INC Ransom ransomware group) |
| Champaign-Urbana Public Health District | IL | Healthcare Provider | 501 | Network server hacking incident |
| The Medical Imaging Partnership dba Precision Imaging Center | FL | Healthcare Provider | 501 | Network server hacking incident |
| Interim HealthCare of Oklahoma City, Inc. | OK | Healthcare Provider | 500 | Email/network server hacking incident (Genesis & Anubis ransomware groups) |
| Pennsylvania Dermatology Partners | MD | Healthcare Provider | 500 | Network server hacking incident |
| Alpine Agency of the Midlands, LLC | SC | Business Associate | 500 | Email hacking incident |
| Family Medical Associates of Raleigh, PA | NC | Healthcare Provider | 500 | Network server hacking incident |
Causes of June 2026 Healthcare Data Breaches
A majority of the data breaches reported in July were due to hacking and other IT-related incidents, including all but one of the 23 data breaches affecting 10,000 or more individuals. In July, 67 of the month’s data breaches (87%) were reported as hacking/IT-related incidents, involving the protected health information of 33,446,371 of the month’s affected individuals (99.9%). The average breach size was 499,200 individuals, and the median breach size was 4,851 individuals.
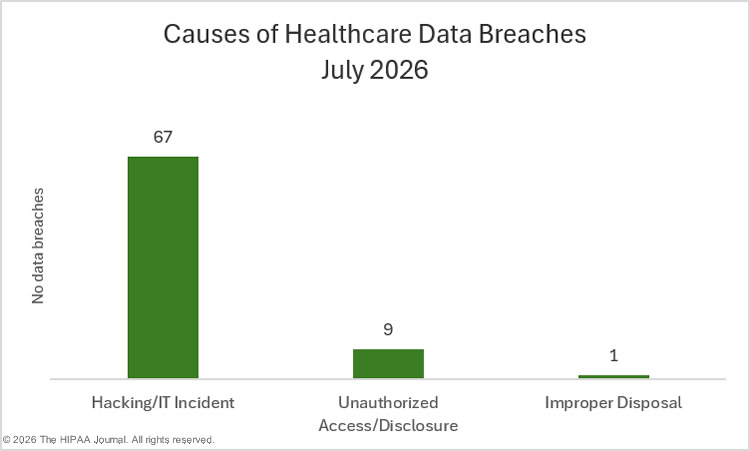
Between January 1 and July 31, 414 hacking/IT incidents were reported – 86% of all data breaches – and they accounted for 97.8% of all affected individuals (65,89,1098 individuals). While the same number of healthcare data breaches have been reported as this time last year, hacking/IT incidents have increased by 7.3% year-over-year.
In July 2026, 9 of the month’s data breaches were reported as unauthorized access/disclosure incidents (11.7% of incidents), involving the protected health information of 23,054 of the month’s affected individuals (0.07%). The average breach size was 2,562 individuals, and the median breach size was 1,680 individuals. Between January 1 and July 31, 62 unauthorized access/disclosure incidents were reported – 12.9% of all data breaches – and they accounted for 2.2% of all affected individuals (1,490,420 individuals). Unauthorized access/disclosure incidents have decreased by 27% year-over-year.
In July 2026, only one of the month’s data breaches was due to the improper disposal of protected health information (1.3%), and that incident affected 16,545 individuals (0.05%). Between January 1 and July 31, 2 improper disposal incidents were reported – 2.6% of all data breaches – and they accounted for 0.03% of all affected individuals (17,545 individuals). Improper disposal incidents have doubled year-over-year.
No loss/theft incidents were reported in July. Between January 1 and July 31, only 2 loss/theft incidents were reported – 0.4% of all data breaches – and they accounted for 0.002% of all affected individuals (1,359 individuals). Loss/theft incidents have decreased by 400% year-over-year.
Location of Breached Protected Health Information
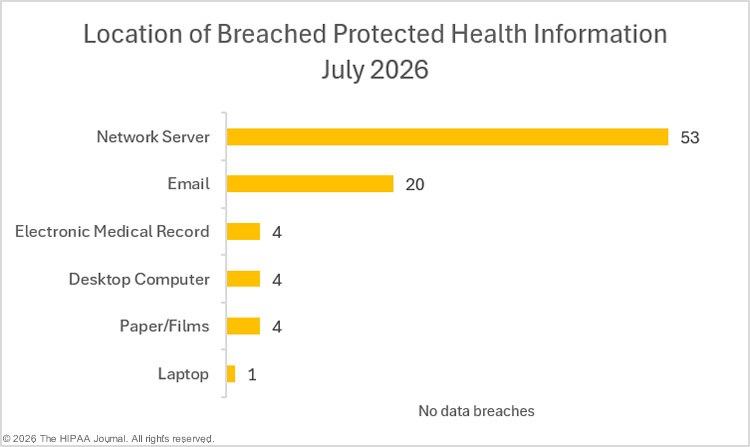
In July, network servers were the most common location of breached protected health information, followed by email systems.
Data Breaches at HIPAA Regulated Entities
The HIPAA Breach Notification Rule requires HIPAA-covered entities to report data breaches to OCR and notify the affected individuals. Notifications must also be issued when there is a data breach at a business associate of a HIPAA-covered entity; however, it is ultimately the responsibility of each affected HIPAA-covered entity to ensure that notifications are issued. A covered entity may delegate the reporting requirements to the business associate that experienced the data breach, or may choose to issue notifications themselves. The raw breach data on the OCR breach portal shows data breaches based on the reporting entity, not where the data breach occurred.
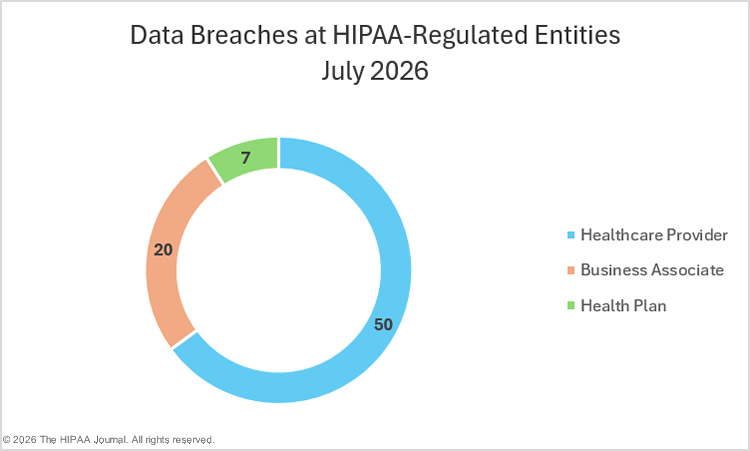
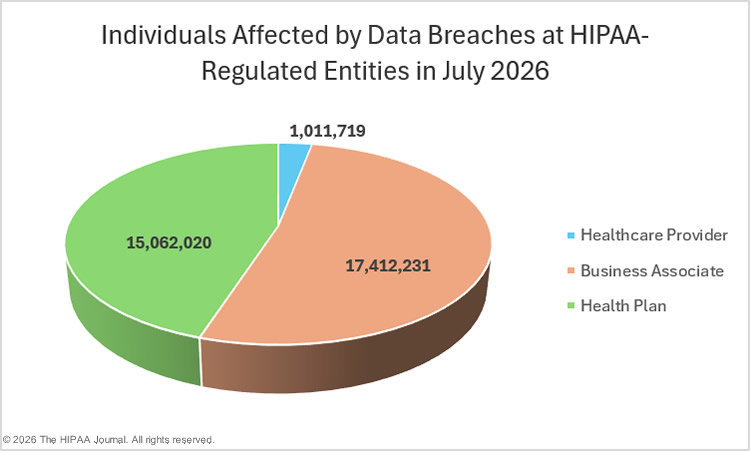
In July, healthcare providers reported 56 data breaches, business associates reported 12 breaches, and 9 breaches were reported by health plans. The pie charts below show where the breach actually occurred rather than the reporting entity to better reflect data breaches at business associates.
Geographical Distribution of Healthcare Data Breaches
In July, large healthcare data breaches were reported to OCR by HIPAA-regulated entities in 30 U.S. states and the District of Columbia. Texas was the worst affected state with 11 large data breaches, closely followed by California with nine.
| State | Breaches | State | Breaches |
| Texas | 11 | Arizona | 1 |
| California | 9 | Connecticut | 1 |
| Florida | 5 | District of Columbia | 1 |
| Massachusetts | 5 | Idaho | 1 |
| Illinois | 4 | Indiana | 1 |
| Minnesota | 4 | Iowa | 1 |
| New York | 4 | Kansas | 1 |
| North Carolina | 4 | Maine | 1 |
| Tennessee | 3 | Maryland | 1 |
| Wisconsin | 3 | Mississippi | 1 |
| Arkansas | 2 | Oklahoma | 1 |
| Michigan | 2 | Pennsylvania | 1 |
| New Jersey | 2 | South Carolina | 1 |
| Ohio | 2 | Virginia | 1 |
| Alabama | 1 | Washington | 1 |
Massachusetts topped the list in terms of affected individuals, with more than 18 million individuals affected across its five data breaches, followed by Alabama, which experienced one data breach that affected more than 9.5 million individuals across the United States.
| State | Individuals Affected | State | Individuals Affected |
| Massachusetts | 15,317,249 | Wisconsin | 18,549 |
| Alabama | 9,540,683 | Minnesota | 15,398 |
| Ohio | 3,805,854 | Maine | 14,830 |
| New Jersey | 3,759,869 | Virginia | 9,909 |
| California | 478,468 | Tennessee | 9,835 |
| Idaho | 88,000 | Michigan | 5,707 |
| Texas | 71,136 | North Carolina | 4,493 |
| Arkansas | 65,520 | West Virginia | 2,173 |
| Florida | 60,164 | Connecticut | 1,556 |
| Illinois | 56,638 | Indiana | 1,530 |
| District of Columbia | 56,197 | Arizona | 800 |
| Mississippi | 30,403 | Iowa | 746 |
| Pennsylvania | 24,496 | Washington | 501 |
| Kansas | 24,088 | Maryland | 500 |
| New York | 19,678 | Oklahoma | 500 |
HIPAA Enforcement Activity in July 2026
OCR announced one HIPAA enforcement action in July to resolve alleged violations of the HIPAA Rules. OSF Healthcare System is a Peoria, Illinois-based integrated health system that serves patients at 174 locations in Illinois and Michigan, including 16 hospitals. OSF Healthcare System was investigated by OCR in response to a reported cybersecurity incident that exposed the protected health information of 53,907 individuals. A ransomware group breached its network, stole patient data, encrypted files, and demanded payment to delete the stolen data and unlock the encrypted files. The attack was discovered by OSF Healthcare System in April 2021.
OCR’s investigators determined OSF Healthcare System failed to conduct a HIPAA-compliant risk analysis, there was an impermissible disclosure of the ePHI of 53,907 individuals, and a failure to provide timely notifications to OCR and the affected individuals. The alleged HIPAA violations were settled, with OSF Healthcare System and its Affiliated Covered Entities agreeing to pay a $552,250 financial penalty and adopt a corrective action plan to address the identified areas of noncompliance.
This was another enforcement action under OCR’s risk analysis enforcement initiative. While OCR has not announced a specific enforcement initiative targeting noncompliance with the HIPAA Breach Notification Rule, OCR appears to be looking closely at HIPAA Breach Notification Rule compliance. Since the start of 2025, eight HIPAA settlements have included penalties for Breach Notification Rule failures.
About this Report
The HIPAA Journal monthly data breach reports are based on data obtained from the HHS Office for Civil Rights and have been combined with breach report data from other sources. The data breaches included in this report were reported in July 2026 but occurred weeks or months previously. The data was obtained from OCR on October 10, 2026. The figures in this report may increase or decrease as HIPAA-regulated entities complete their breach investigations, and those changes will be reflected in our healthcare data breach statistics page and our annual HIPAA data breach reports. Further information about HIPAA enforcement actions can be found in our HIPAA violations cases page.





